





-
A hidden chip in compromised Ledger Nano X devices reportedly captured 24-word recovery phrases and transmitted them via LTE.
-
Estimated losses range from $84.2M to $103M, while Tether froze $10M in USDT.
-
Ledger described the incident as a physical supply-chain attack, not a software breach.
Ledger revealed that a secret chip embedded in hardware wallets from its reseller CryptoBilis captured 24-word recovery phrases from the screen and transmitted them via the cellular network to the attacker, which researchers estimated to cost between $84.2 million and $93.2 million.
The French firm revealed the details of the attack vector for the first time in a blog post update on X on Tuesday made by its security team, Ledger Donjon. This is perhaps the most detailed explanation of how the owners of the compromised devices lost access to their cryptocurrency without even touching Ledger’s software.
How the implant pulled keys off the screen
The additional chip was located inside the device’s housing, according to Ledger. While setting up the wallet, when the user shows the 24 words that serve as a backup for the account, the microcontroller of the implant reads them and translates them into data that is transmitted over LTE via an integrated SIM card.
Such a recovery code is basically an account. With its help, you can restore your wallet on another piece of hardware without having to use the compromised device and perform any transactions.
Update on Ledger devices at MediaMarkt Saturn 🔽
As of Oct. 13th, MediaMarkt Saturn has stopped, with Ledger’s alignment, the sale of Ledger devices in their stores and online while the investigation continues, following the report of an implant from one customer in Germany. No loss of funds were reported.
We have no indication that Ledger’s infrastructure, systems or services were compromised. Ledger Support is reviewing user reports, and Ledger’s cybersecurity experts, the Donjon will be examining the devices we receive: https://t.co/QzukOZdEzq.
If you have questions about a device you bought, contact Ledger Support at https://t.co/QzukOZdEzq. Ledger will never call you, message you directly or ask for your 24-word recovery phrase.
Many claims and figures circulating online are unverified. Scammers often try to take advantage of incidents like this. Rely only on official Ledger and MediaMarkt Saturn channels for updates. We will share more as the investigation continues.
— Ledger (@Ledger) October 13, 2026
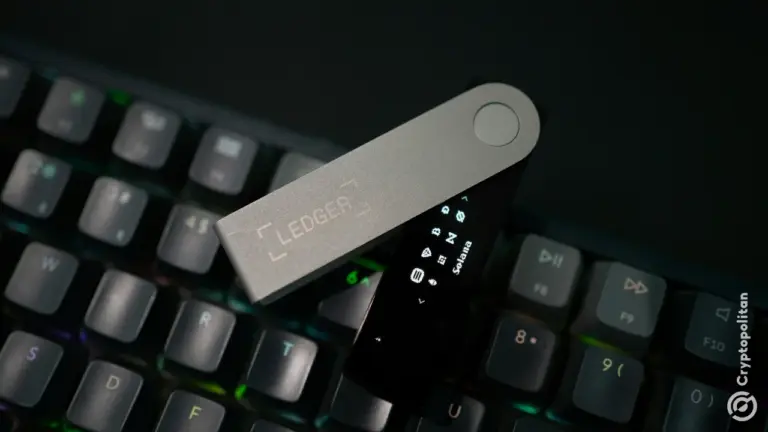
According to reports, the hacked devices were the Ledger Nano X model. Mark Karpelès, former CEO of Mt. Gox and now at Karpeles Lab, shared a picture of the implant hidden behind the screen and noted that the antenna cable of the latter was the clue. The research laboratory Tibane Labs confirmed the discovery and said it had two versions of the implant, including one with an ST STM32G431KBU6 microcontroller, a 2×2 mm eSIM, and an LTE module.
A supply-chain attack, not a software breach
However, Ledger made sure to outline what was spared by the attack. The implant didn’t harm the Secure Element, the chip that ensures the safety of private keys. It didn’t affect the operating system, and it had no impact on transactions and signatures, as stated by the company in its X post.
The company characterized the incident as a physical attack on its supply chain and not a hacking incident against its software or internal processes. Ledger, the company claims that it ships more than 8 million devices, pointed out that its “Genuine Check” system is unable to detect any implant while the original Secure Element remains untouched.
Ledger theft estimates top $86M as Tether blocks $10M
Ledger has not released any data on the number of victims or the value involved. However, on-chain research firms have done their work and arrived at their numbers. Reports say that about $93.2 million in losses are spread through more than 300 wallets. But investigator Specter puts the losses beyond $86 million, and Yfarmx increases its figure to $103 million. Tether is freezing $10 million worth of its USDT stablecoin associated with the theft.
This was discovered on October 9 when Ledger started an investigation into the alleged funds draining and asked CryptoBilis to stop selling its signers. Ledger revealed on October 10 that one of the compromised users’ devices contained an illegal implant. So far, all of the losses confirmed involve a unit sold by CryptoBilis, an authorized reseller in Indonesia, Malaysia, and the Philippines.
Rivals cut ties with CryptoBilis
CryptoBilis reportedly stopped all of its sales and deliveries of hardware wallets of different brands in the three countries and closed down its brick-and-mortar stores, expanding on an earlier move that involved the Ledger brand alone. The reseller company stated that it was reviewing the situation with the help of outside experts.
Trezor stated that it did not see any evidence of tampering with its devices resold by CryptoBilis, yet decided to remove the reseller from its list of authorized distributors. OneKey company stated that there were no losses reported to be associated with this case and also removed CryptoBilis from its list of authorized resellers; additionally, it offered free replacement for OneKey devices purchased via CryptoBilis between March 1 and October 12, 2026.
Reports beyond the reseller
“Ledger said it is investigating reports of implants in devices not sold by CryptoBilis, but it has not confirmed yet a theft in a device purchased from any other store,” reported Cointelegraph. In addition, according to Cointelegraph, there was an X user named Johannes who uploaded pictures of two Ledger devices which he claims were purchased separately from MediaMarkt stores in Europe and both were implanted.
Ledger has not yet confirmed any connection between the reports in Europe and the CryptoBilis case. The advice for the users of CryptoBilis products, according to Ledger, is very clear: do not initialize a signer from CryptoBilis and if you have initialized one, then move funds to another device with a new recovery phrase.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
FAQs
How did the CryptoBilis implant steal crypto?
A microcontroller hidden inside the device read and decoded the 24-word recovery phrase shown on screen during setup, then sent it to attackers over an LTE mobile network using an embedded SIM, according to Ledger. The recovery phrase alone lets an attacker rebuild the wallet and move the funds.
How much was stolen in the Ledger CryptoBilis attack?
Ledger has not confirmed a figure, but on-chain researchers estimate between $86 million and $103 million, with CoinDesk citing up to $93.2 million across more than 300 wallets. Tether has frozen $10 million of USDT tied to the theft.
What should buyers of CryptoBilis wallets do now?
Ledger says not to initialize a signer bought from CryptoBilis, and anyone who already set one up should move assets to a new device with a newly generated recovery phrase. It also advises contacting support and filing a police report.
Disclaimer. The information provided is not trading advice. Cryptopolitan.com holds no liability for any investments made based on the information provided on this page. We strongly recommend independent research and/or consultation with a qualified professional before making any investment decisions.

Ashish Kumar
Ashish Kumar is a crypto and financial journalist with eight years of newsroom experience. He covers what’s happening with crypto markets, regulation, DeFi, and exchange ecosystems. He has worked with Coingape, Todayq, and Newsroompost. Ashish holds a PGDP in English Journalism from the IIMC. He has also interviewed industry figures including Arthur Hayes, Yat Siu, Austin Federa, and more.









