




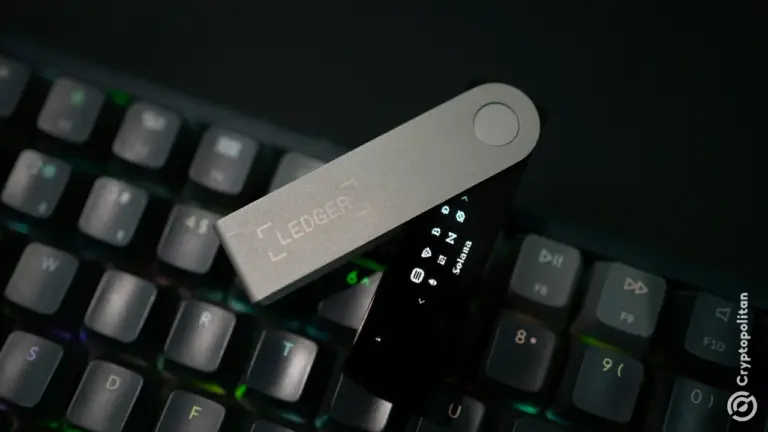
- Ledger is investigating reports that more than $86 million in Bitcoin, Ethereum and Tron was stolen from wallets sold through CryptoBilis, a reseller the company had authorized.
- The losses undercut Ledger’s advice to buy only from approved channels.
- The scare lands while the firm is attempting to attract private investors after shelving its $4 billion IPO.
Ledger has opened an investigation into the theft of about $86 million. The money was allegedly stolen from crypto wallets sold through CryptoBilis.
The company’s standard safety advice is to buy only from vetted, official channels like CryptoBilis, which was vetted by Ledger itself.
How much was stolen from Ledger’s reseller?
CryptoBilis is a Malaysian online store launched in December 2020 by Arravind Prabu, Vimal Selvamany and Dhivager Rathakrishnan, under their company, Fetch International. The store said in 2021 that it became an authorized reseller for the Paris-based hardware wallet maker.
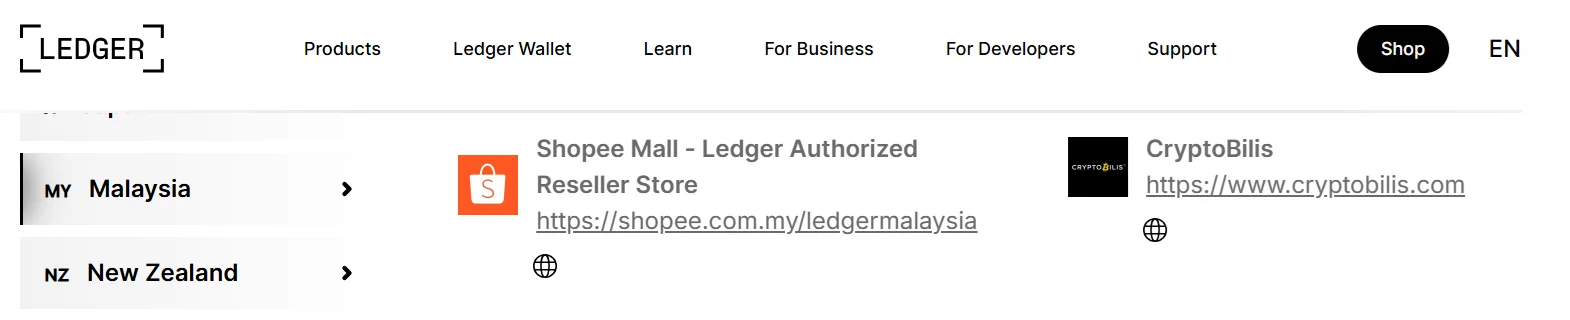
On Friday, Ledger said on its support account that it had asked CryptoBilis to halt all sales and shipments of Ledger products while it investigates reports that more than $86 million in Bitcoin, Ethereum and Tron was stolen from wallets the store sold.
Specter, a pseudonymous blockchain investigator, posted on X that there had been complaints of drained wallets across X and Reddit among Ledger owners.
Specter said their investigation into the suspected theft addresses found deposits arriving from hundreds of victim wallets on Bitcoin, Ethereum and Tron, adding up to more than $86 million.
The total amount lost in the hack and any connection between the individual cases have not been confirmed. The cause is also still unknown. Ledger says there is no evidence that its own systems or wallet software were breached.
Ledger advised anyone who bought from the reseller in the past 90 days not to set up their device yet. Customers who had already activated a wallet were told to move their funds to a different Ledger device with a newly generated recovery phrase.
What are the leading theories?
One popular theory for how the attackers carried out the hack is a supply-chain attack. In this attack, a device is tampered with such that whatever recovery phrase used for it is already known to an attacker before it reaches the buyer. The attacker can then drain the wallet once funds land on it.
This method was documented in 2023 when Kaspersky researchers found a tampered Trezor Model T hardware wallet. The device’s main chip had been replaced, and its software was rigged so that it gave users one of 20 phrases already known to the attackers. The attackers waited about a month before emptying the wallet in this case.
Cryptopolitan reported that Ledger abandoned a planned $4 billion U.S. IPO in May, saying the decision was due to poor market conditions. The company said it was weighing private fundraising instead, but the chances now seem slim with this fresh security scare.
Ledger recorded a separate incident in January, disclosing that its payment processor Global-e experienced a customer-data leak. Investigator ZachXBT commented on the incident, saying that hardware wallet firms cannot be trusted with personal information.
Don’t just read crypto news. Understand it. Subscribe to our newsletter. It's free.
FAQs
How much crypto was reportedly stolen and from where?
Specter, a pseudonymous investigator, said on X that more than $86 million was traced from hundreds of victim wallets across Bitcoin, Ethereum and Tron, though the figure has not been independently confirmed.
What should people who bought a Ledger from CryptoBilis do?
Ledger advised buyers from the past 90 days not to set up their devices, and said anyone who already activated a wallet should transfer their assets to a new Ledger device using a newly generated recovery phrase.
Was Ledger's own technology hacked?
Ledger said there is no evidence its systems or wallet software were compromised; the investigation concerns devices sold through a third-party reseller, with a supply-chain attack cited as one possible but unconfirmed explanation.
Disclaimer. The information provided is not trading advice. Cryptopolitan.com holds no liability for any investments made based on the information provided on this page. We strongly recommend independent research and/or consultation with a qualified professional before making any investment decisions.

Hannah Collymore
Hannah is a writer and editor with nearly a decade of blog writing and event reporting experience in the crypto space. At Cryptopolitan, Hannah contributes to the news page, reporting and analyzing the latest developments in DeFi, RWA, crypto regulation, AI and frontier tech industries. She graduated from Arcadia university with a degree in Business Administration.









